 a27f4ec402
Some checks are pending
Build and Test / Secret Scan (push) Waiting to run
Build and Test / Detect changed areas (push) Waiting to run
Build and Test / Provider pair Docker acceptance (push) Blocked by required conditions
Build and Test / Frontend (push) Blocked by required conditions
Build and Test / Compile backend race tests (no execution) (push) Blocked by required conditions
Build and Test / Backend tests (rest-0) (push) Blocked by required conditions
Build and Test / Backend tests (rest-1) (push) Blocked by required conditions
Build and Test / Backend tests (api-0) (push) Blocked by required conditions
Build and Test / Backend tests (api-1) (push) Blocked by required conditions
Build and Test / Backend tests (api-2) (push) Blocked by required conditions
Build and Test / Backend tests (api-3) (push) Blocked by required conditions
Build and Test / Backend tests (api-4) (push) Blocked by required conditions
Build and Test / Backend tests (api) (push) Blocked by required conditions
Build and Test / Script smoke tests (shard 0/2) (push) Blocked by required conditions
Build and Test / Script smoke tests (shard 1/2) (push) Blocked by required conditions
Build and Test / Script smoke tests & backend build (push) Blocked by required conditions
Build and Test / Benchmarks (push) Blocked by required conditions
Canonical Governance / governance (push) Waiting to run
Canonical Private Governance / private-governance (push) Waiting to run
Provider MSP startup / Provider MSP production startup (push) Waiting to run
Public docs / check (push) Blocked by required conditions
Public docs / Documentation recipes (0) (push) Waiting to run
Public docs / Documentation recipes (1) (push) Waiting to run
Public docs / Documentation recipes (2) (push) Waiting to run
Public docs / Documentation recipes (3) (push) Waiting to run
Core E2E Tests / Playwright Core E2E (shard 7/8) (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 8/8) (push) Blocked by required conditions
Core E2E Tests / Agent registration lifecycle (push) Blocked by required conditions
Core E2E Tests / E2E verdict (push) Blocked by required conditions
Core E2E Tests / Validate E2E tier selection (push) Waiting to run
Core E2E Tests / Offline Organization provisioning (push) Waiting to run
Core E2E Tests / Build source-bound E2E images once (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 1/8) (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 2/8) (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 3/8) (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 4/8) (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 5/8) (push) Blocked by required conditions
Core E2E Tests / Playwright Core E2E (shard 6/8) (push) Blocked by required conditions
## What changes for users First-run setup has a **Usage statistics** switch. If you turn it off on a server started with `PULSE_TELEMETRY=false`, which is the usual choice for privacy-minded Docker users, setup said: > Your admin account was created, but usage statistics could not be turned off. You can turn them off in Settings → System → General. That was false. Statistics were already off: the server refuses the write only because `PULSE_TELEMETRY` locks the setting. Settings can't change a locked value either. After a refused opt-out, setup now checks what the server actually keeps: | Server | Message after opting out | | --- | --- | | `PULSE_TELEMETRY=false` | None. Statistics are off. | | `PULSE_TELEMETRY=true` | "Usage statistics stay on because this server sets PULSE_TELEMETRY=true. Set PULSE_TELEMETRY=false and restart Pulse to turn them off." | | No lock, or the state can't be read | The existing message, unchanged | The `true` case says to set `false` rather than remove the variable, because removing it restores the default, which is on. ## How - **`SecurityStep.tsx`:** when the opt-out write fails, `readTelemetryOutcome()` reads `GET /api/system/settings` (`telemetryEnabled` and `envOverrides`) and picks the message. - **Catalog:** new key `setup.security.error.telemetryLockedOn` in English, German and Spanish. The variable name stays untranslated. ## Verification - **Tests:** - `SecurityStep.test.tsx` covers the locked-off case (no message) and the locked-on case (the new message), and the existing failure test still passes. Its mock is now reset between tests so queued responses can't leak. - `i18n.test.ts` requires `PULSE_TELEMETRY=false` in every locale. - The three new tests fail against `main`. - The i18n, setup wizard and settings localization suites pass (151 tests). - tsc, prettier and the copy, canonical-platform and form-label audits are clean. - **Live:** a fresh instance with `PULSE_TELEMETRY=false`, run through setup with statistics switched off at 1280px and at 375px. The settings write returned 409, the settings read returned 200, no message appeared, and setup continued to "Connect your first system". The phone layout had no sideways scroll. - **Receipt:** the browser receipt is included. |
||
|---|---|---|
| .devcontainer | ||
| .github | ||
| .husky | ||
| cmd | ||
| deploy | ||
| dev/oidc | ||
| docs | ||
| frontend-modern | ||
| internal | ||
| pkg | ||
| scripts | ||
| testdata | ||
| testing-tools | ||
| tests | ||
| .air.toml | ||
| .dockerignore | ||
| .env.example | ||
| .gitattributes | ||
| .gitguardian.yaml | ||
| .gitignore | ||
| .gitleaks.toml | ||
| .gitleaksignore | ||
| .golangci.yml | ||
| .markdownlint-cli2.jsonc | ||
| .markdownlint.json | ||
| analyze_coverage.py | ||
| ARCHITECTURE.md | ||
| CONTRIBUTING.md | ||
| cr.yaml | ||
| docker-compose.yml | ||
| docker-entrypoint.sh | ||
| docker-healthcheck.sh | ||
| Dockerfile | ||
| go.mod | ||
| go.sum | ||
| install.sh | ||
| LICENSE | ||
| Makefile | ||
| package-lock.json | ||
| package.json | ||
| playwright.config.ts | ||
| README.md | ||
| SECURITY.md | ||
| TERMS.md | ||
| VERSION | ||
Pulse

Real-time Proxmox, Docker and Kubernetes monitoring that finds what needs attention.



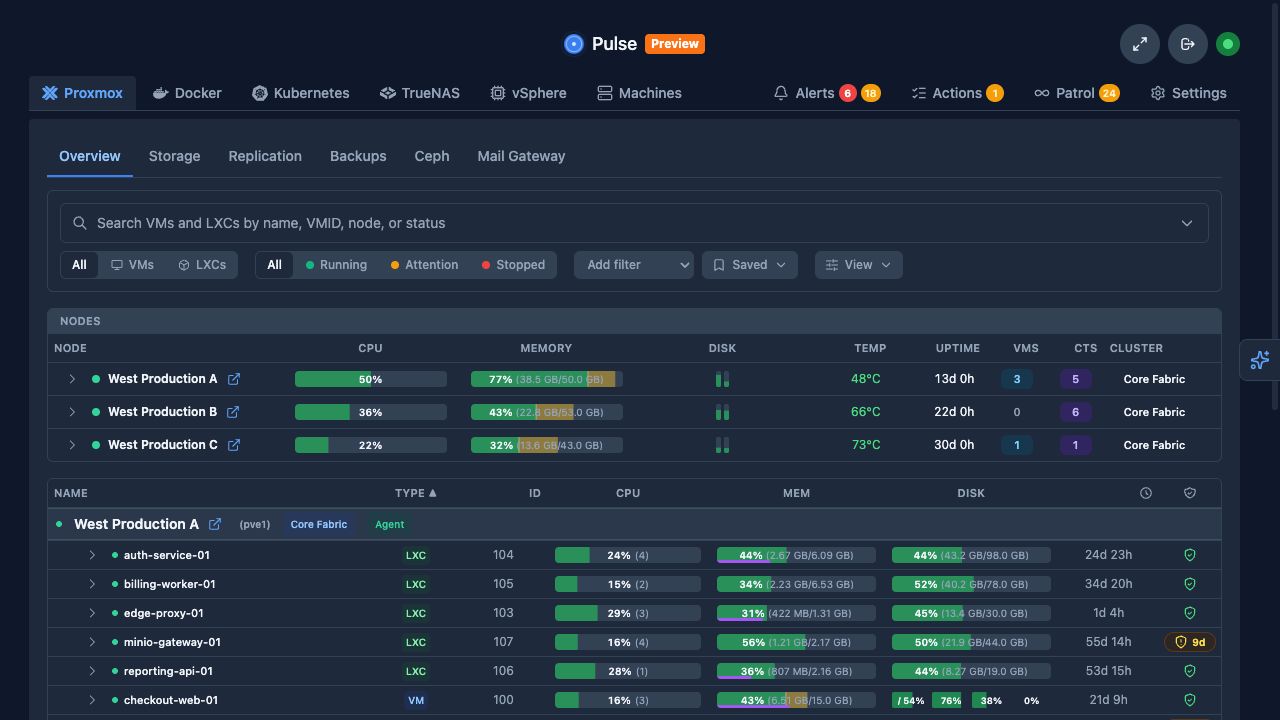
Pulse is a self-hosted monitoring workspace for Proxmox, Docker, Kubernetes, TrueNAS, physical and virtual machines, and early-access VMware vSphere environments. It combines live infrastructure state, history, alerts, recovery visibility, and scheduled health checks without requiring a conventional enterprise monitoring stack.
Why Pulse
- It watches between visits. Alerts and Pulse Patrol find failed backups, capacity pressure, restart loops, unhealthy containers, clock drift, and other problems that dashboards cannot surface when nobody is looking.
- It keeps each platform familiar. Proxmox, Docker, Kubernetes, TrueNAS, vSphere, and machines have dedicated views, backed by one shared resource model for search, alerts, history, and investigation.
- It stays operator-controlled. Credentials are encrypted at rest, API tokens are scoped, agent commands are disabled by default, and governed fixes require the configured policy and approval path.
Platform coverage
| Platform | Coverage |
|---|---|
| Proxmox VE, PBS, and PMG | Nodes, guests, storage, backups, replication, Ceph, mail gateways, and alerts |
| Docker and Podman | Hosts, containers, Compose projects, Swarm services, health, images, and updates |
| Kubernetes | Clusters, nodes, workloads, pods, services, storage, and events through the unified agent |
| TrueNAS SCALE and CORE | Pools, datasets, disks, snapshots, replication tasks, apps, VMs, and alerts |
| Linux, Windows, and macOS machines | Host health, filesystems, networking, temperatures, RAID, and availability through the unified agent |
| VMware vSphere | Early-access inventory, hosts, clusters, VMs, datastores, networks, snapshots, and recovery context; validate against your own vCenter before production use |
Platform pages keep storage and recovery information beside the infrastructure it belongs to. Alerts, Actions, and Patrol remain cross-platform views.
Patrol: monitoring that does rounds
Pulse Patrol runs scheduled checks across the current state and recent history of your infrastructure. Community installations can use a local model or their own AI provider for watch-only analysis. Pulse Pro adds investigation and policy-bound fixes with approval, verification, and an audit trail.

Pulse also includes an interactive Assistant and an MCP adapter for external clients such as Claude Code and OpenCode. Both sit on top of the same scoped inventory, metrics, alert, storage, and governed-action contracts.
Quick start
Choose an exact version from the latest release and keep that version pinned during installation.
Docker
docker run -d \
  --name pulse \
  -p 7655:7655 \
  -v pulse_data:/data \
  -e PULSE_DEPLOYMENT_METHOD=docker_run \
  --restart unless-stopped \
  rcourtman/pulse:vX.Y.Z
Open http://<your-ip>:7655 and follow the bootstrap-token setup. Docker host
monitoring is provided by the unified agent; the Pulse server container does
not need the Docker socket.
Proxmox LXC, Linux, and Kubernetes
The installer is signed. Verify install.sh against the pinned
pulse-installer key before running it:
export PULSE_VERSION=vX.Y.Z
curl -fsSLO "https://github.com/rcourtman/Pulse/releases/download/${PULSE_VERSION}/install.sh" &&
curl -fsSLO "https://github.com/rcourtman/Pulse/releases/download/${PULSE_VERSION}/install.sh.sshsig" &&
ssh-keygen -Y verify \
  -f <(printf '%s\n' 'pulse-installer namespaces="pulse-install" ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIMZd/DaH+BldzOkq1A8KVTcFk73nAyrE8aJOyf7i00jm pulse-installer') \
  -I pulse-installer \
  -n pulse-install \
  -s install.sh.sshsig < install.sh &&
bash install.sh --version "${PULSE_VERSION}"
Paste the whole block: installation stops if either download or signature verification fails. Do not run the final command separately to bypass a failure.
The GitHub installer installs the Pulse server. Install and upgrade agents (including v5-to-v6 agent upgrades) with the per-host command generated under Settings → Infrastructure → Install on a host.
Do you need an agent?
Often not. Proxmox VE, PBS, and PMG are monitored through the Proxmox API with a read-only token, so no Pulse host agent is required. The generated setup script creates a privilege-separated monitoring user. Install the unified agent only where you want data the platform API cannot provide, such as host SMART health, temperatures, Docker hosts, or standalone machines.
API-only does not mean guest-agent-free. VM filesystem and memory requests through QEMU Guest Agent can share the channel used by freeze-enabled backups. Read-only permissions do not prove backup safety. Do not add permissions, enable or restart an agent, or send manual guest-agent probes during a backup, freeze or thaw. Use the existing backup safety precaution. Stopping Pulse also stops its monitoring and alerts. An OK backup task does not prove successful thaw.
The agent is operator-controlled by design. Command execution is off by
default, the local listener binds to localhost, and generated systemd units
ship hardened. On Linux, the installer's --least-privilege profile runs the
service as a dedicated non-root user, with optional scoped sudo grants for
the few collectors that need elevation. The
agent security model documents exactly what the
agent can and cannot do at each privilege level.
Important
GitHub release assets and
rcourtman/pulseimages are Community builds. Relay, Pro, and eligible legacy customers should use the private image or Linux archive provided by the Pulse download portal. Replacing a private Pro runtime with a public Community build removes its private runtime hooks.
Editions
- Community — self-hosted monitoring, seven days of metric history, core SSO, update alerts, and Patrol with your own provider or local model.
- Pro — Community plus Patrol investigation, governed fixes, ninety days of history, centralized agent profiles, RBAC, audit logging, and reporting.
- MSP — for managed service providers: one Pulse Account running many client workspaces, each with an isolated Pulse runtime — separate dashboards, alerts, users, audit history, and reports. Free sixty-day two-client evaluation at Pulse for MSPs.
Relay is no longer sold. Existing Relay subscribers receive Pro features at their current price for as long as their subscription continues. Existing paired phones keep working until 31 March 2027. Relay connects the app, not the web UI. Use your own VPN or tunnel for remote web access. For phone alerts, add an ntfy, Gotify or Pushover destination and open Pulse in your phone's browser.
Core self-hosted monitoring is not gated by monitored-system or child-resource volume. See the runtime-aligned capability reference and current plans for details.
Documentation
- Install and deployment
- Production deployment and security
- Upgrade from Pulse v5
- Releases and update channels
- Configuration
- Platform and agent guides
- Pulse Intelligence
- Security and privacy
- Code signing policy
- Troubleshooting
- API reference and architecture
Localized getting started guides: Deutsch · Español
Development
Pulse uses Go 1.26 and a SolidJS/TypeScript frontend. The managed development
runtime starts the frontend at http://127.0.0.1:5173 and proxies API and
WebSocket traffic to the backend on port 7655.
npm ci
npm --prefix frontend-modern ci
npm run dev
Useful checks:
go test ./...
npm --prefix frontend-modern test
npm --prefix frontend-modern run type-check
python3 scripts/check_public_docs.py
See CONTRIBUTING.md before investing in a code change. Pulse uses an issue-first contribution process and does not normally accept unsolicited pull requests.
Community and support
- Ask questions in GitHub Discussions.
- Report bugs and unexpected outcomes through GitHub Issues.
- Home Assistant users can use the community-maintained Pulse add-ons.
- If Pulse is useful to you, support its development through GitHub Sponsors or Ko-fi.
Read the safe reporting guidance before sharing original evidence. A second reproduction or diagnostics export is not required; do not repeat an attempt that could interrupt workloads or send duplicate notifications. GitHub reports and attachments are public: review them locally and keep credentials and private details out.
License
Everything in this repository is licensed under the MIT License. There is no dual licensing and no commercial or source-available code here.
Pulse Pro is a separate commercial product, built from private sources and distributed through pulserelay.pro. Its use is governed by the Terms of Service, which apply to that product only, not to anything in this repository.